
What is risk management? It is a coordinated system to identify, assess, prioritize, mitigate, monitor, and review threats to an organization’s capital, operations, and reputation. The pressure is real in 2026, because the market for risk management has already moved into strategic territory, not back-office paperwork, and global volatility is still rising across enterprises.
The high-stakes problem is this. Many firms still treat risk as a static checklist, yet cross-border business punishes static thinking first. A contract that looks fine in one jurisdiction can fail under another legal regime, while a compliance process that works domestically can leave a multinational exposed abroad.
The High-Stakes Reality of Risk Management in 2026
The old assumption says risk management belongs to compliance teams and annual reviews. That assumption is now dangerous. The global risk management market was valued at USD 13.86 billion in 2020, and one projection places it at USD 35.9 billion by 2032 (worldmetrics.org). That kind of growth reflects a hard truth, large organizations now treat risk as a strategic investment, especially in finance, insurance, supply chains, and cross-border operations.
Volatility also stays inside the organization, not just outside it. In a 2025 Ponemon insider-threat dataset cited in 2026 industry reporting, mistaken or negligent insiders accounted for 4,321 incidents, averaging 13.5 incidents per organization, with losses of USD 676,517 per incident (secureframe.com). At the same time, 80% of enterprise risk management decision-makers said volatility is increasing or staying the same, with 44% saying it is increasing and 36% saying it is staying the same (secureframe.com).
Static registers fail in dynamic businesses
A risk register helps only if people update it. Cross-border companies add new entities, vendors, data flows, and contract structures constantly, so yesterday’s assessment goes stale quickly. ISO 31000’s emphasis on systematic, timely, and responsive risk management matters here, because a frozen register creates false comfort.
Practical rule: if the business changed, the risk picture changed too.
For multinational clients, continuity planning also sits inside risk management, not beside it. A useful parallel is this complete guide to continuity management, because continuity planning forces leaders to ask who acts, when they escalate, and what fails first. That same discipline helps legal teams stop treating disruption as a surprise event.
Mistake is reacting only after damage appears. The better model is ex-ante legal mitigation, where contract design, escalation rights, and internal controls absorb pressure before it becomes a dispute. In a cross-border environment, that difference is the gap between controlled exposure and expensive improvisation.
The Risk Management Lifecycle Explained
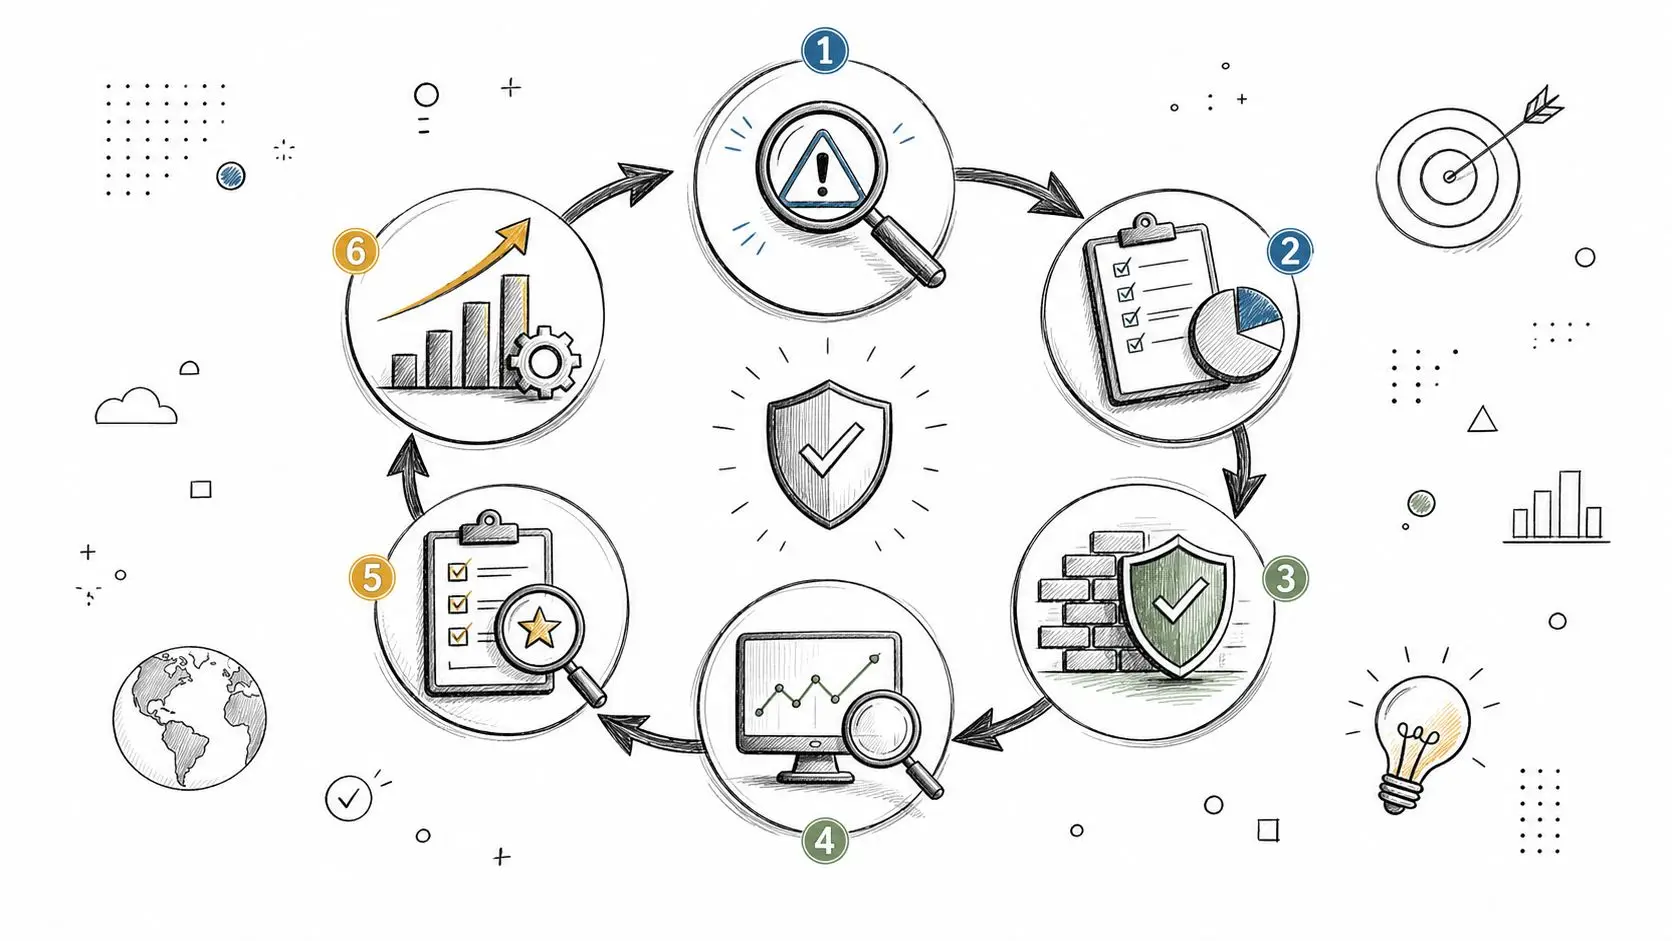
Risk management works when it moves in a sequence, but that sequence stays iterative. Identify the exposure, assess its likelihood and impact, prioritize it, treat it, monitor results, then review again when the business changes. The UK government’s Orange Book frames risk management as coordinated activities tied to internal control and informed by the best available information and expertise (gov.uk).
Identify the risk before the dispute frames it for you
Identification must go beyond a generic list. In practice, that means interviewing commercial leaders, reviewing contracts, mapping data flows, and asking where a counterparty can create delay, exert power, or cause non-payment. NIST’s assessment cycle starts with establishing context and identifying assets and data flows, which is exactly the right mindset for legal teams handling regulated or cross-border exposure (HHS NIST guidance).
Assess likelihood and impact in legal terms
Assessment should not stop at a vague red, amber, green chart. Counsel should translate each risk into legal and financial consequences, such as injunction exposure, termination rights, forum risk, or recoverability of damages. ISO 31010 supports this discipline with tools such as bow-tie analysis, FMEA, fault tree analysis, event tree analysis, and Bayesian methods, because each method maps cause, consequence, likelihood, and residual exposure differently (WCO guidance).
Prioritize and treat the risk
Prioritization should direct attention to risks that can disrupt the business. Fast triage tools work well for obvious issues, while deeper analysis fits interacting failures and hidden dependencies. Treatment can include contract clauses, governance protocols, insurance, operational redesign, or escalation triggers, depending on where the exposure sits.
Monitor, review, and reset
Monitoring matters because risk scores decay. A new supplier, cloud service, regulator, or distribution route changes the baseline. In information and data risk contexts, NIST recommends layered controls such as access restriction, encryption, masking, quarantine, deletion, and continuous discovery scans, then periodic reassessment as conditions change (HHS NIST guidance).
The best programs treat risk as a pipeline, not a spreadsheet.
A practical KPI set also helps. Operational teams often track the total risks identified, the percentage mitigated, mitigation timeline, and business cost associated with risk. Those metrics force accountability, because they show whether controls reduced exposure or just created paperwork.
Classifying Corporate Risks in a Global Context
Corporate risk categories only work if they reflect how risks collide. A contract breach can trigger financial loss, supply interruption, and reputational damage at the same time. Likewise, a cyber issue can become a compliance event the moment personal data crosses borders or a regulator asks where the data sat and who controlled it.
Cross-border operations blend every category
Legal risk sits at the center because it changes how every other risk resolves. A payment dispute may be financial on paper, but it can become a jurisdiction fight, a collection problem, or a distribution failure. Reputational exposure also moves quickly, because counterparties, banks, and regulators often judge the event before the facts are fully developed.
| Corporate Risk Categories and Cross-Border Implications | ||
|---|---|---|
| Risk Category | Primary Drivers | Cross-Border Legal Implications |
| Legal | Contract breach, regulatory conflict, weak escalation rights | Forum disputes, unenforceable clauses, fragmented remedies |
| Financial | Non-payment, FX pressure, credit stress | Collection delays, asset location issues, recovery uncertainty |
| Operational | Vendor failure, logistics breakdown, internal process gaps | Performance disputes, supply interruption, service liability |
| Reputational | Public conflict, media coverage, stakeholder distrust | Brand damage across jurisdictions, negotiation leverage loss |
| Cyber | Unauthorized access, weak controls, third-party exposure | Data breach notification, privacy obligations, evidence handling |
| Compliance | Sanctions, privacy, anti-corruption, sector rules | Overlapping regulatory obligations, local-law conflicts |
| Cross-border | Entity structure, data flow, local counsel gaps | Enforcement problems, translation issues, inconsistent remedies |
The most common mistake is siloing these categories. Teams label a matter “legal” and stop there, or call it “operational” and ignore the contract. That creates blind spots. ISO 31000’s named principles, including integrated, inclusive, dynamic, and continual improvement, address exactly that failure mode (Vector Solutions).
Legal exposure often determines the real loss
Risk categories also overlap in loss severity. A weak indemnity can turn a manageable supply incident into a full-cost dispute. A narrow dispute resolution clause can shift advantage to the counterparty. A poor governing-law choice can make enforcement slower, more expensive, or strategically weaker.
In multinational work, the legal label rarely matches the commercial damage.
For that reason, multinational risk reviews should always ask one extra question. If this issue escalates, which jurisdiction controls the remedy, and which party can move faster? That answer often matters more than the initial incident.
Practical Frameworks for Legal Risk Mitigation
ISO 31000 is useful because it treats risk management as an organization-wide discipline, not a compliance ritual that sits apart from the business. Its principles, integrated, structured and customized, inclusive, dynamic, based on the best available information, human and cultural factors, and continual improvement, give legal teams a drafting and governance framework that can be used in cross-border matters. That matters in Israeli and multinational work, where the legal fix has to work before the dispute, not after the filing.
Contract design should allocate failure, not just describe it
Good contracts do more than restate commercial intent. They allocate failure before the dispute starts. Force majeure clauses should fit the actual supply chain, indemnities should match the actual loss channel, and dispute resolution clauses should reflect where the counterparty assets, witnesses, and influence sit.
A few drafting choices matter every time:
- Force majeure: define the events narrowly enough to prevent abuse, but broadly enough to cover genuine delivery failure.
- Indemnity: tie the trigger to a real risk source, such as IP infringement, data misuse, or regulatory breach.
- Dispute resolution: choose the forum that makes enforcement realistic, not just familiar.
- Termination rights: preserve exit rights where performance risk or compliance risk becomes unacceptable.
Governance turns clauses into action
A strong clause still fails if no one escalates the issue. Governance should define who receives notice, who can suspend performance, who can approve settlement, and who owns external counsel instructions. In multinational structures, that allocation often breaks down because operational teams expect legal to react, while legal expects business teams to escalate.
Draft for the failure mode, not the ideal relationship.
The NIST cycle helps here as well. Better asset visibility reduces unknown exposure, control coverage lowers exploitability, and regular reassessment prevents stale risk scoring (HHS NIST guidance). The same logic applies to contracts and governance, because a clause without monitoring is only a promise.
A practical option for clients building this structure is RNC Group, which handles international commercial disputes, crisis response, and multilingual legal coordination. That kind of support matters when the file needs both legal sequencing and cross-border execution, not a generic review. For related operational planning, supply chain risk mitigation strategies can help frame how logistics failures, vendor screening, and continuity planning affect whether a contract problem stays contained.
Real-World Case Examples in Cross-Border Disputes
An anonymized franchise dispute shows the difference between prevention and reaction. A foreign franchisor entered Israel with a contract that named local law, but it left operational standards vague and under-described the audit process. When performance slipped, both sides argued over standards, notice, and cure rights, and the dispute moved from operations into enforcement.
The winner usually prepared the record first
The better-positioned party in these disputes usually documented performance early. It kept written notice clean, preserved correspondence, and escalated before the relationship collapsed. That simple discipline often determines whether a matter ends in a negotiated exit or prolonged litigation.
A different case involved a distribution relationship across two jurisdictions. The contract had commercial detail, but it lacked a credible escalation ladder. When payment delays started, the supplier sent threats too late, and the distributor used the delay to pressure pricing, inventory, and credit terms. The legal issue was payment, yet the business loss came from failed risk management.
For supply-related exposure, a useful external reference is supply chain risk mitigation strategies. That resource aligns well with legal work because logistics failures, vendor screening, and continuity planning often determine whether a contract problem stays contained or spreads.
Generic frameworks miss the human move
Cross-border cases also expose the limits of standard risk registers. A partnership may look stable on paper while internal expectations change, the market shifts, or one side takes a public position that the other side cannot absorb. Recent practitioner coverage notes that predefined lists can miss non-obvious threats and strategic concerns that do not fit standard categories (Carrier Management).
That is exactly why jurisdiction-specific counsel matters. Local procedure, evidence handling, and enforcement mechanics change the strategy. A one-size-fits-all framework can help organize thought, but it cannot replace legal execution.
A dispute often turns on who understood the leverage first.
Actionable Checklists for International Expansion
International expansion fails when teams sign first and assess later. The better approach is to build the risk file before market entry, then keep revising it as the structure, counterparties, and regulatory footprint change. In practice, the legal team should treat that file as a live control system, not a one-time memo.
Pre-expansion checklist
- Map the entity structure: identify who contracts, who invoices, and who carries liability.
- Review governing law and forum clauses: test whether they support practical enforcement.
- Confirm local regulatory overlap: check privacy, data transfer, sanctions, tax, and sector rules.
- Prepare contract templates: include indemnity, limitation, audit, and termination language.
- Set escalation owners: name who approves suspension, notice, and settlement.
These items are not generic housekeeping. They determine whether a dispute can be contained at the contract stage or spreads across affiliates, vendors, and local regulators. For an Israeli business entering multiple jurisdictions, the wrong entity structure or forum clause can turn a recoverable problem into an enforcement fight.
Clause library to prepare in advance
The contract pack should include a force majeure clause, a confidentiality clause, a data handling clause, a payment security clause, and a dispute resolution clause. Each clause should answer one question clearly. What happens, who pays, who acts, and where the dispute goes.
That drafting work should also reflect the transaction. A payment clause that looks acceptable in one market may fail if local rules limit setoff, withholding, or security arrangements. A dispute clause that is easy to sign may be harder to enforce if evidence, service, or interim relief must be handled abroad.
Crisis workflow to keep ready
A crisis workflow should include notice deadlines, document preservation rules, external counsel instructions, and media approval lines. It should also identify when to move from business negotiation to formal demand, because delay can destroy negotiating power. That matters in cross-border matters, where service rules and enforcement timelines vary, and where a local procedural mistake can weaken the entire position.
Escalate early, document everything, and keep one factual version.
Preparation costs less than correction. The right checklist does not eliminate risk, but it reduces surprise, shortens response time, and gives the legal team room to negotiate from strength. That is the return on legal risk management when the business is crossing borders and the exposure is legal as much as commercial.
Next Steps for Engaging Specialized Counsel
Risk management becomes most effective when counsel gets involved before the problem hardens into a dispute. Specialized cross-border lawyers can align contracts, escalation rights, and enforcement strategy from the start, which often matters more than post-incident cleanup. For multinational businesses, that is the difference between controlled exposure and a costly scramble.
RNC Group advises on international commercial risk, dispute strategy, and crisis response with a cross-border execution focus. For businesses facing Israeli or multinational exposure, the recommended strategic path is to review the contract, forum, and escalation structure before the dispute matures, then act on the weakest point first. Visit RNC Group or contact the firm now at RNC Group contact page to discuss the next step.
Disclaimer: This article provides general information only and does not constitute legal advice. Readers should not rely on it for any specific matter without obtaining jurisdiction-specific advice from qualified counsel.