
A multinational board that still treats sanctions as a checklist is preparing for the wrong dispute. In 2026, the more dangerous trigger may be a lawful-looking transaction that later becomes the center of frozen funds, blocked payments, broken contracts, and cross-border litigation.
That risk is acute for Israeli businesses and foreign corporations with Israeli operations. Israel sits inside dense trade, technology, finance, and logistics networks, so a weak sanctions risk assessment doesn’t stay inside compliance. It spills into banking relationships, shareholder claims, supply disputes, insurer notice fights, and emergency court applications across several jurisdictions.
Your Next Lawsuit May Not Involve a Contract
What if your next major lawsuit starts with a payment hold, a bank escalation, or a counterparty ownership surprise rather than a breach notice?
Boards that still treat sanctions as an operations problem are inviting preventable litigation. A failed sanctions risk assessment sets off the chain. Funds are frozen. Banks restrict access. Distributors suspend performance. Insurers reserve rights. Directors are then asked why the company approved the transaction without identifying the exposure points that any serious review should have caught.
This matters acutely in the Israeli cross-border context. Israeli companies operate through dense networks of foreign banks, dollar payments, cloud services, logistics providers, and multinational counterparties. One weak assessment can trigger disputes in Israel, the UK, the EU, and the U.S. at the same time. The legal problem spreads faster than management can contain it.
Why boards misread the threat
The first warning sign rarely arrives in legal language. It appears as a delayed remittance, an unexplained compliance questionnaire, a customer suspension, a lender inquiry, or a shipment that stops moving.
Management then loses valuable time arguing over labels. Finance treats it as a payments issue. Sales treats it as a customer issue. Operations treats it as delay. Outside institutions move first, create the record, and define the crisis before the company has chosen its own position.
Boards should classify this as enterprise legal risk and move it beyond a narrow compliance silo.
That recommendation is practical, not academic. A sanctions failure often becomes the factual basis for claims that sit far beyond the sanctions rule itself. Counterparties sue over non-performance. Banks defend freezes and exits. Shareholders challenge oversight. Joint venture partners allege disclosure failures. In Israel, where companies routinely contract across multiple legal systems, one missed sanctions issue can mature into parallel proceedings, urgent injunction work, and expensive forum fights.
Directors who need a basic reference point can review VolunteerBadge’s OFAC guide, then insist on a board-level framework built for cross-border disputes rather than checklist screening.
What a failed assessment actually causes
A weak assessment misses more than a name match. It misses how exposure enters the commercial structure and where litigation will follow if the transaction stalls.
Common failures include:
- Counterparty design: No serious review of beneficial ownership, control rights, nominee structures, or sanctioned touchpoints hidden inside affiliates.
- Transaction design: Payment routes, currencies, intermediaries, and service providers were approved without analyzing which jurisdictions and institutions they pull into the deal.
- Contract design: Agreements omit sanctions representations, information covenants, audit rights, suspension rights, and termination language that can be enforced under pressure.
- Governance design: No one owns escalation when an alert appears, an ownership profile changes, or a bank asks questions that signal a larger problem.
Boards should treat sanctions risk assessment as part of the company’s legal infrastructure for market access, payment collection, and defensible decision-making. If that infrastructure fails, the company may still hold a signed agreement and still lose the ability to perform, get paid, ship goods, or keep core banking channels open.
That is the point boards miss. The immediate loss is operational. The lasting damage is legal.
Mapping The Global Sanctions Landscape
How does an Israeli company end up in cross-border litigation when the underlying deal looked lawful at signing?
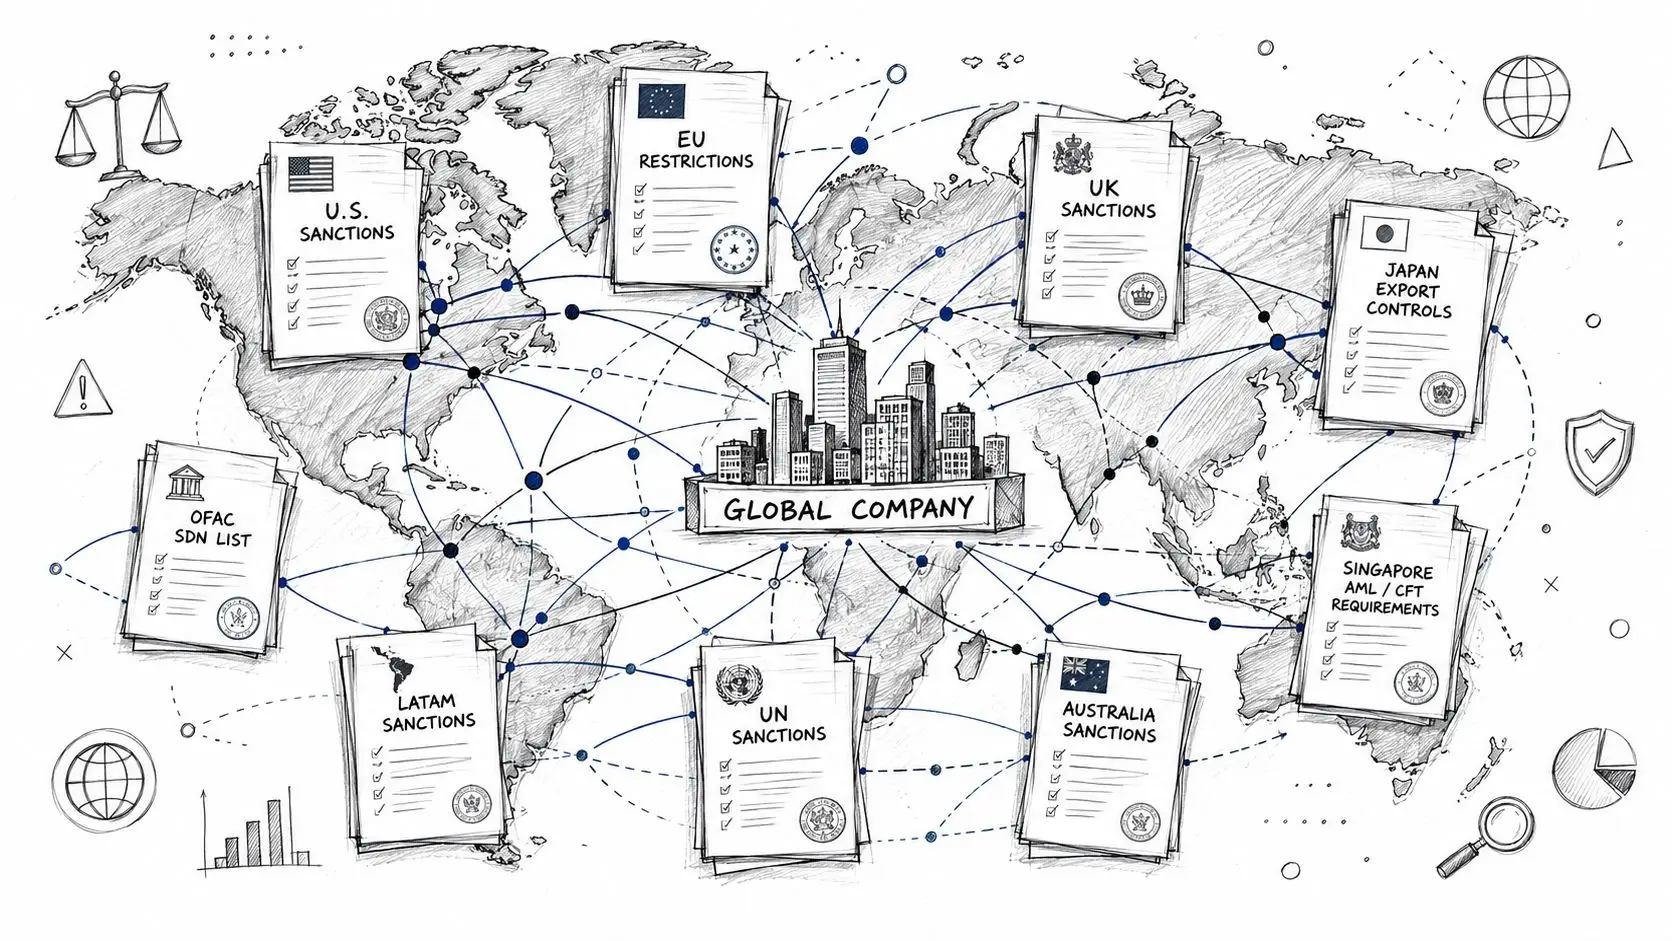
It happens when management treats sanctions as a screening issue instead of a jurisdictional one. An Israeli business can satisfy local requirements and still trigger restrictions under U.S., EU, UK, or UN regimes because the transaction touches a foreign bank, a dollar payment route, a cloud provider, an investor, or a distributor outside Israel. That mismatch is where commercial disputes start.
Overlap creates the litigation risk
Boards should stop asking which sanctions regime matters most. The right question is simpler and harder. Which regimes attach to this deal once money moves, goods ship, services are delivered, and counterparties start asking their banks for clearance?
Foreign exposure enters through ordinary commercial design:
- Payment mechanics: U.S. dollar clearing, correspondent banks, intermediary institutions, or settlement through an international financial group.
- Territorial connections: Goods, services, personnel, or performance obligations tied to the EU, UK, U.S., or UN-linked jurisdictions.
- Technology infrastructure: Hosting, software access, servers, support functions, or data flows that create cross-border contact.
- Ownership and control: Parent companies, affiliates, nominees, beneficial owners, or investors behind the visible counterparty.
Even operational teams need a working grasp of this structure. For a basic introduction to one major regime, many companies begin with VolunteerBadge’s OFAC guide. The legal task then becomes transaction-specific analysis, not generic screening.
A company’s customers, banks, suppliers, and payment routes determine its intersection with sanctions law, regardless of management’s intent.
The Israeli cross-border lens
Israeli businesses face this problem more often than they admit. A typical deal may combine Israeli founders, foreign venture investors, U.S. dollar invoices, European customers, offshore developers, regional distributors, and cloud infrastructure hosted elsewhere. Each connection can import a different sanctions regime into the same commercial relationship.
That is why failed sanctions assessments so often mature into multi-jurisdictional litigation. A bank freezes payment. A supplier suspends performance. A customer invokes termination rights. An insurer questions coverage. A joint venture partner alleges misrepresentation. The dispute then spreads across contracts, forums, and governing laws because the original assessment never identified which foreign restrictions could disable performance.
The right question for directors
Directors should retire the question, “Do we do business with sanctioned countries?” It is too blunt to protect revenue, banking access, or litigation posture.
They should ask:
- Which sanctions regimes attach to our revenue model, payment flows, and service delivery chain?
- Where can hidden ownership, control rights, or affiliate relationships import sanctions exposure into an otherwise ordinary deal?
- Which business lines could produce a payment block, shipment delay, contract suspension, or post-closing dispute if a counterparty is challenged?
- Which decisions must be escalated to legal immediately because they affect future defensibility in court, arbitration, or a regulatory inquiry?
A sanctions risk assessment that cannot answer those questions is not a control system. It is evidence for the other side once the transaction fails.
A Practical Risk Assessment Framework
A defensible sanctions program needs structure, not slogans. The market has plenty of broad guidance and very little disciplined execution. Boards should insist on a model that can be documented, challenged, and repeated.
A sanctions risk assessment is typically built in three stages: inherent risk, control effectiveness, and residual risk. For many institutions, the cycle repeats every 12 to 18 months, depending on risk profile and regulatory expectations, as described by ACAMS on effective and current sanctions risk assessments.
The three-stage model
The first stage measures exposure before controls. The second tests whether existing controls do reduce that exposure. The third decides what risk remains and whether that remaining level is acceptable.
| Assessment Stage | Objective | Key Questions to Address |
|---|---|---|
| Inherent Risk | Identify where sanctions exposure exists before mitigation | Which customers, products, geographies, payment channels, and third parties create direct or indirect exposure? |
| Control Effectiveness | Evaluate the strength of existing controls | Are screening, onboarding, escalation, training, and recordkeeping documented, tested, and reliable? |
| Residual Risk | Determine the risk that remains after controls apply | Which exposures still threaten banking access, contractual performance, or regulatory defensibility? |
What directors should demand at each stage
The first stage must inventory the business as it operates. Legal entities, customers, products, services, supply chains, and geographies all matter. A company that reviews only formal counterparties is understating its exposure from the start.
The second stage must test controls against the identified risks. That means documented screening logic, ownership review procedures, alert handling, staff accountability, and evidence that the business doesn’t rely on assumptions. If a control exists only in policy language, it doesn’t exist.
Practical rule: Score exposure where the business earns money, moves money, and depends on money. Those are usually the places where sanctions failures become lawsuits.
The third stage is where boards often fail. They accept a residual rating without asking whether controls map to each identified risk. That is backwards. Residual risk should follow from demonstrated mitigation, not managerial optimism.
Quantification matters
A robust approach converts qualitative exposure into a quantified inherent-risk score and then calculates residual risk by mapping each inherent risk to documented controls, as explained in Protiviti’s sanctions risk management framework. That is how a company shows its model is defensible rather than decorative.
The point isn’t mathematical elegance. The point is legal credibility.
Boards should ask for evidence on these issues:
- Data integrity: Are customer, supplier, ownership, and payment records complete enough to support screening?
- Scope: Does the model cover suppliers, customers, products, services, geography, and data-feed reliability?
- Control mapping: Can management show which control mitigates which risk?
- Escalation linkage: Does the assessment trigger remediation, retraining, or transaction blocking when needed?
Reassessment is governance, not administration
Sanctions risk changes when the business changes. New markets, new owners, new channels, new suppliers, and new payment routes all affect the model.
A board should therefore require a living assessment cadence, event-driven updates, and immediate reassessment after any material shift in operations or counterparties. The legal value of the assessment lies in its currency. Once it goes stale, it loses predictive force and evidentiary value at the same time.
Implementing Essential Mitigation Controls
A good assessment identifies risk. A serious program reduces it. The distinction matters because courts, regulators, banks, and counterparties judge conduct by controls in operation, not by policy language.
The strongest programs use risk-based segmentation. High-risk relationships trigger enhanced due diligence, escalated review of complex ownership structures, and more frequent monitoring, while lower-risk segments receive standard controls, according to ApexAnalytix on sanctions risk assessment practices.
Start with counterparties, not software
The first control is disciplined KYC and KYB. Name screening alone is inadequate. The business must understand who owns the counterparty, who controls it, what it does, and how it gets paid.
For higher-risk relationships, standard onboarding isn’t enough. Management should require deeper ownership review, supporting corporate documents, and heightened scrutiny of unusual structures, intermediaries, or payment instructions.
A useful regional perspective appears in Comfi’s analysis of combating financial crime in MENA trade. It highlights why trade flows, counterparties, and finance channels in the region require joined-up review rather than siloed checks.
Contracts are a sanctions control
Commercial lawyers often underuse the contract as a sanctions defense. That is a mistake with expensive consequences.
A well-drafted agreement should allocate compliance duties, require prompt disclosure of ownership changes, preserve audit rights where appropriate, and create clear suspension or termination rights when sanctions concerns arise. Those protections matter in distribution, supply, service, and property relationships alike. They also reinforce wider commercial risk planning in documents such as a commercial lease agreement.
If a counterparty becomes high risk after signing, the company needs a contract that permits action before the relationship becomes a dispute.
Layer the controls
No single measure will carry the program. Boards should require layered controls that work together:
- Due diligence depth: High-risk parties need enhanced review, not recycled onboarding forms.
- Screening discipline: Automated tools are useful, but trained personnel must review alerts and resolve ambiguity.
- Transaction review: Payment anomalies, routing changes, and unusual instructions need a hold-and-escalate process.
- Contractual safeguards: Agreements should create disclosure duties and clean exit options before a crisis starts.
The legal objective is simple. Force risk to surface early, while the company still controls the transaction and the evidence.
Operational Integration For Defensibility
A sanctions risk assessment that sits in a presentation deck has no legal value. It becomes useful only when the company embeds it into daily decisions, clear authority lines, and auditable records.
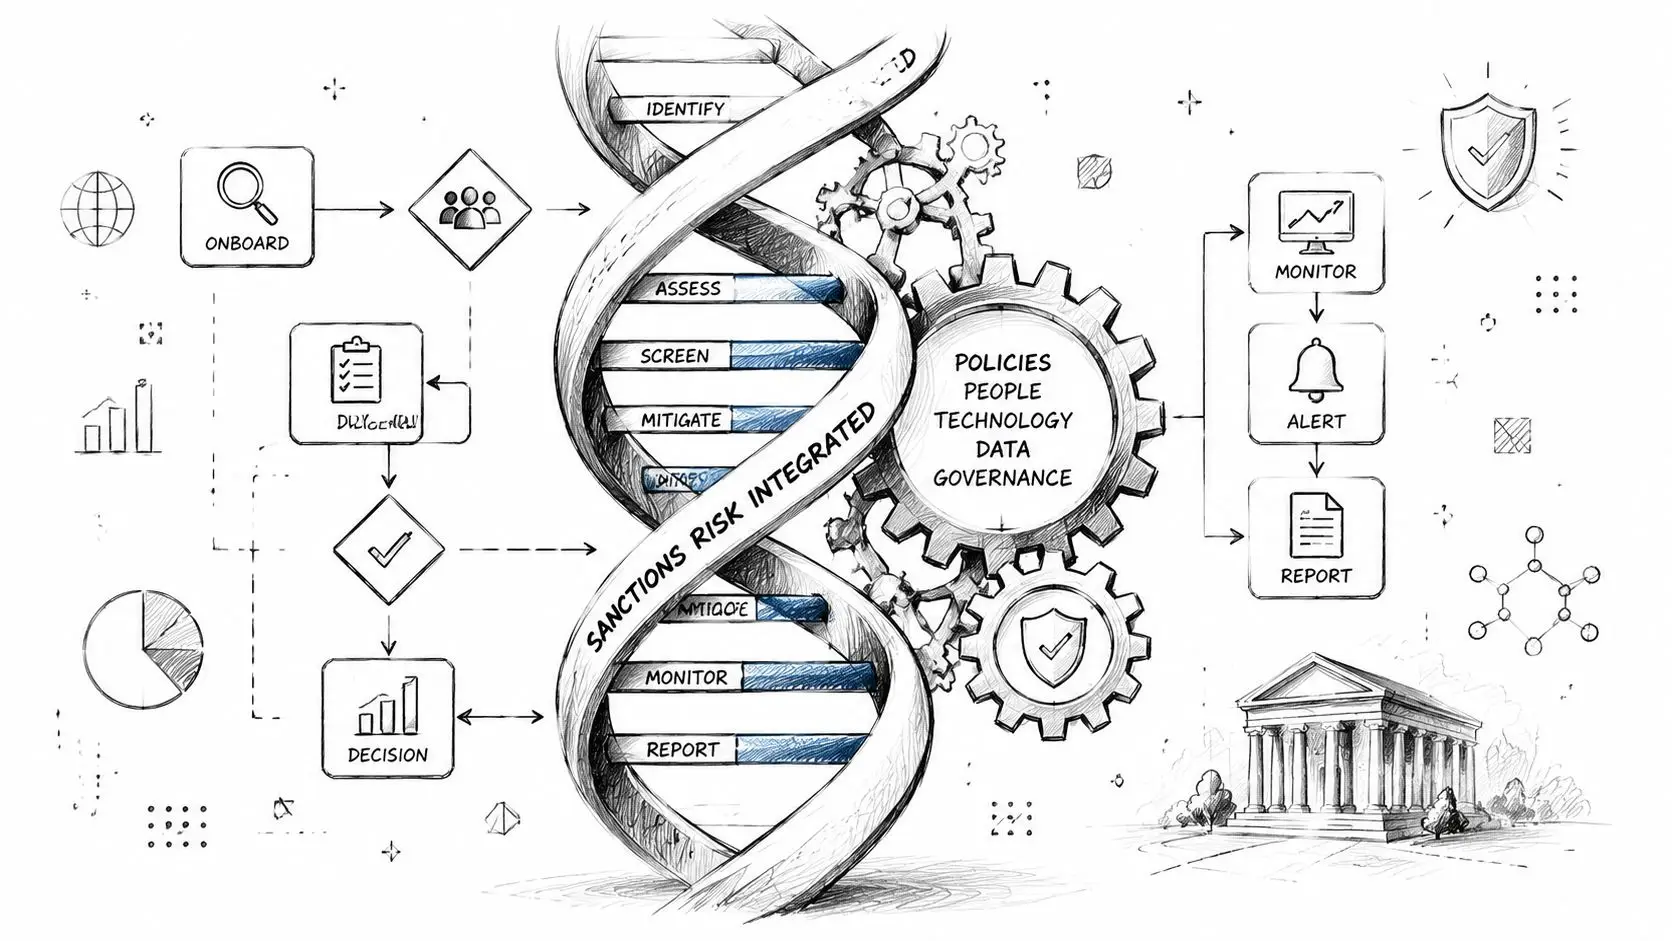
Current guidance keeps stressing a major gap. Many firms know the factors to review, yet they still struggle to turn qualitative screening into a defensible, quantitative risk model, and the operational metrics that best predict breaches or alert quality remain under-answered, as discussed by Sanctions.io on building a sanctions risk score.
Assign owners and authority
Every multinational board should know who owns sanctions risk. If that answer is vague, the program is weak.
The company needs defined responsibility for onboarding review, alert investigation, legal interpretation, payment blocking, and final escalation. It also needs authority rules. Someone must have the power to stop a transaction quickly, without waiting for committee drift.
That structure should appear in policy, workflow, and training. If the process exists only in the heads of a few employees, it will collapse during pressure.
Build escalation before the crisis
A potential sanctions hit can become a crisis within hours. The business may face a bank freeze, a blocked payment, an anxious customer, and urgent internal questions at the same time.
That is why sanctions escalation should connect to a broader crisis management protocol. The company must know when legal steps in, when external counsel or foreign advisers are engaged, who communicates with the bank, and how privilege is preserved during internal fact gathering.
The difference between a manageable incident and a destructive one is often procedural speed. Companies lose ground when alerts drift between compliance, finance, and sales.
Keep records as if litigation is inevitable
Recordkeeping isn’t administrative overhead. It is evidence.
The company should be able to show why it approved, paused, investigated, or rejected a transaction. That includes screening outputs, ownership reviews, alert notes, escalation logs, and final decision records. If a bank later imposes restrictions or blocks activity, those records become central, especially where issues overlap with bank account blockages.
Operational defensibility depends on routine discipline:
- Policies must match reality: Written procedures should reflect actual workflow and actual approval authority.
- Training must be role-specific: Sales, finance, procurement, legal, and operations don’t face the same red flags.
- Escalation must be tested: Teams should rehearse how to handle urgent alerts and ambiguous ownership findings.
- Audit trails must be complete: Every material decision should leave a clear documentary path.
A one-time assessment gives comfort. Integrated operations give protection.
Scenarios For Israeli Cross-Border Businesses
The value of a sanctions risk assessment appears when it changes operational decisions before legal damage starts. Two common Israeli business profiles show why generic compliance language isn’t enough.
An Israeli SaaS company with a global user base
A software company may believe it carries low sanctions risk because it ships no physical goods. That assumption is dangerous. Digital delivery doesn’t remove sanctions exposure. It changes the routes through which exposure enters.
The inherent risks usually sit in customer onboarding, payment processing, reseller channels, user geography, and corporate account ownership. A sanctioned connection may appear through a parent entity, an affiliate, a channel partner, or a payment path that sales never reviewed.
A serious assessment would ask hard questions. Which jurisdictions create customer concentration risk? Which enterprise accounts deserve enhanced ownership review? Which technical controls can block access from prohibited locations? Which teams can suspend an account before revenue recognition creates internal resistance?
The control response should be equally concrete:
- Onboarding controls: Screen corporate customers, not just account names. Review ownership and control where regional sensitivity or complex structures appear.
- Technical controls: Restrict access where geographic exposure requires it. Align those restrictions with legal review and logging.
- Commercial controls: Insert sanctions compliance obligations into enterprise terms, partner agreements, and channel arrangements.
- Escalation controls: Give legal and compliance authority to freeze activation, renewals, and payout activity.
If the company skips that architecture, the dispute won’t stay inside compliance. The bank may question incoming payments. A reseller may claim wrongful suspension. A customer may allege discriminatory termination. Investors may ask why management lacked a documented basis for its decisions.
An Israeli manufacturer sourcing abroad and selling into Europe
A manufacturer faces a different pattern. The legal danger often sits in the supply chain, goods classification, freight route, distributor network, and settlement process.
The inherent-risk review should focus on supplier ownership, origin data, logistics intermediaries, end-user uncertainty, and payment routing. The company must understand more than who supplies the component. It must understand who stands behind the supplier, who moves the goods, and where the money travels.
The control response should include:
- Supplier diligence: Verify legal identity, beneficial ownership, and business activity before procurement approval.
- Contract discipline: Add sanctions representations, change-notice duties, and termination rights in purchasing and distribution agreements.
- Transaction gating: Hold unusual routing requests, substituted consignee details, or unexplained bank changes for legal review.
- Renewal review: Reassess existing suppliers and distributors when ownership, geography, or transaction patterns shift.
Sanctions risk often translates into litigation risk. A shipment delay can trigger a contract claim. A blocked payment can trigger a debt dispute. A distributor cut off for compliance reasons may allege bad faith or wrongful termination. If management cannot show a documented, proportionate, and consistently applied sanctions framework, its litigation position weakens immediately.
The board-level conclusion
Both examples make the same point. A sanctions risk assessment is not a checklist for auditors. It is a litigation-prevention tool, a banking-protection tool, and a market-access tool.
Boards should demand a model suited to the business, tied to contracts, integrated into transactions, and supported by records that can survive scrutiny in more than one jurisdiction. Anything less leaves the company exposed at the exact moment speed, evidence, and legal clarity matter most.
Costly mistakes usually begin with small assumptions. The recommended strategic path is to address sanctions exposure before a bank freeze, contract collapse, or regulator inquiry forces reactive decisions. Businesses operating across Israel and foreign markets can contact RNC Group now to assess vulnerabilities and structure a defensible cross-border response.
This article provides general information only and doesn’t constitute legal advice. Sanctions exposure is fact-specific, jurisdiction-specific, and highly sensitive to timing, counterparties, and transaction structure. Any decision should follow legal advice specific to the relevant facts, jurisdictions, and contractual framework.